EMPOWERING YOUR DIGITAL FUTURE
Secure your infrastructure 24/7 – with minimal effort for your team
On this page you get an overview of our services around secure networks, monitoring & Network Operations Center (NOC), managed services and attack detection systems (SzA) in line with BSI requirements.
sichere Netzwerke, Monitoring & Network Operations Center (NOC),
Managed services and attack detection systems (SzA) in line with BSI requirements.
Our focus: critical infrastructures & secure networks
Whether KRITIS operator, mechanical engineering or mid-sized manufacturing: we are your partner when availability, security and transparency in the network are business-critical.
Our core customers are mainly critical companies, e.g.:
- Electricity and gas utilities
- Telekommunikationsunternehmen
- Einrichtungen im Gesundheitswesen (insbesondere Krankenhäuser)
Beyond that we support numerous mid-sized customers, for example from mechanical and plant engineering, manufacturing industry and service providers.
When designing networks we follow the guidelines of the BSI, in particular the guideline ISi-LANA (Secure connection of local networks to the internet).

Key principles we consistently apply from these guidelines:
-
No direct routing from the internet into the local network
– Every connection runs through defined security zones and gateways. -
Strict service separation
– Critical services are separated logically and physically, e.g. separation of management, server and user networks. -
Vendor break
– We deliberately use different manufacturers in critical chains (e.g. internet firewall from vendor A, internal firewall from vendor B). -
Logging & monitoring as a must, not a nice-to-have
– All security-relevant components are centrally monitored and evaluated.
At the same time we help our customers to meet ISO 27001 requirements and BSI specifications more easily – especially in the environment of KRITIS and the IT Security Act 2.0.
How we build infrastructure
P-A-P-Sicherheitskonzept – erklärt wie am Flughafen
How we build infrastructure
P-A-P-Sicherheitskonzept – erklärt wie am Flughafen
Our security concept typically follows a P-A-P approach:
Portfilter – Application Layer Gateway – Portfilter
Instead of explaining it in a highly technical way, we like to use the airport analogy:
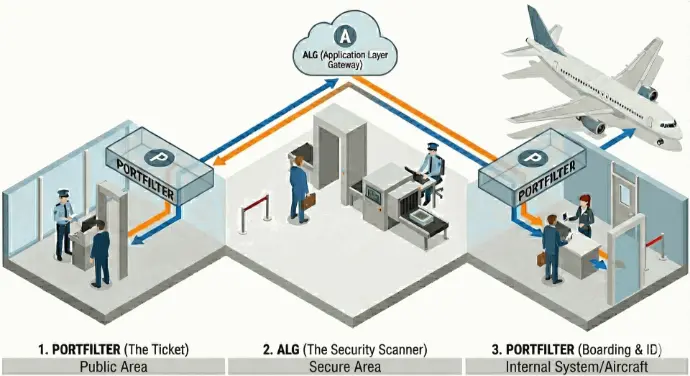
- First packet filter = your flight ticket at the airport entrance
- Without a ticket you do not even get into the airport area.
- Applied to IT: the first packet filter (firewall) decides which connections get through from outside to the security zone at all.
-
Application Layer Gateway = security check with scanner
- Here you go through the scanner, your luggage is X-rayed, prohibited items are sorted out.
- Applied to IT: the Application Layer Gateway inspects the actual content of the connection (e.g. HTTP, DNS, mail) and only lets through what we want.
-
Zweiter Portfilter = Ticket + Ausweis beim Einstieg ins Flugzeug
- Before you board the plane, ticket and ID are checked once more.
- Applied to IT: a further packet filter protects the internal network and ensures that only defined, checked connections reach the target system.
Advantages summarised clearly for managers:
- Multi-layered protection instead of „one big firewall and done“
- Better controllable risks through clear zones and roles
-
Implementable in line with BSI guidelines (ISi-LANA), i.e. audit-proof for audits and certifications
Monitoring & Network Operations Center (NOC)
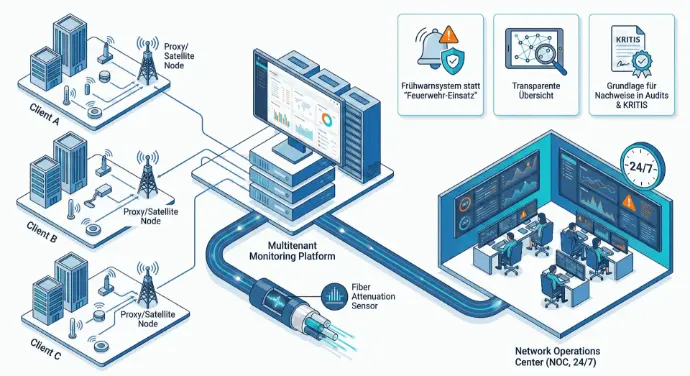
Alongside our managed-service business we have built a highly developed monitoring system:
- Multimandanten-fähige Monitoring-Plattform
- Use of proxy / satellite nodes at the customer site
- Capture of a wide range of sensor data – down to fibre-optic attenuation
- Tight integration with our Network Operations Center (NOC, 24/7)
Your benefit:
- Frühwarnsystem statt „Feuerwehr-Einsatz“
- Transparent overview of the state of your networks and systems
- Basis for evidence in audits and KRITIS reviews
Bereitschaftsdienst & Alarmmanagement
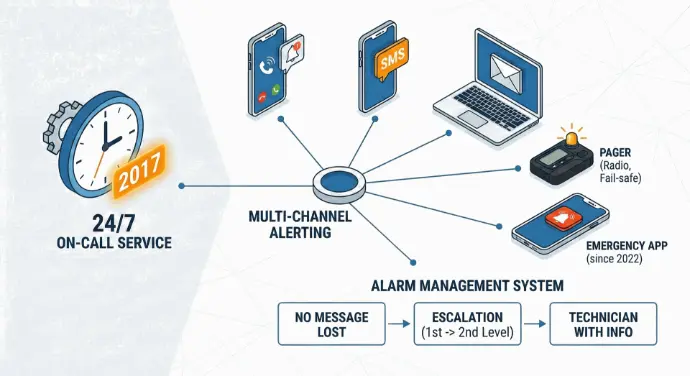
Already since 2017 we have introduced a structured on-call service to react to incidents outside business hours too.
Our alerting concept includes:
-
Mehrkanal-Alarmierung
- Mobilfunk (Anruf/Push)
- SMS
- Pager (Funkmeldeempfänger)
- since 2022 additionally an emergency app for smartphones
What is a pager?
A pager is a small, robust radio receiver that reliably receives short messages or alarm codes.
Through a sophisticated alarm management system we ensure that:
- keine Meldung verloren geht,
- Eskalationen automatisch ablaufen (z. B. 1st Level → 2nd Level),
- the right technician is supplied as quickly as possible with all necessary information.
Central Operations Dashboard (COD) by extocode
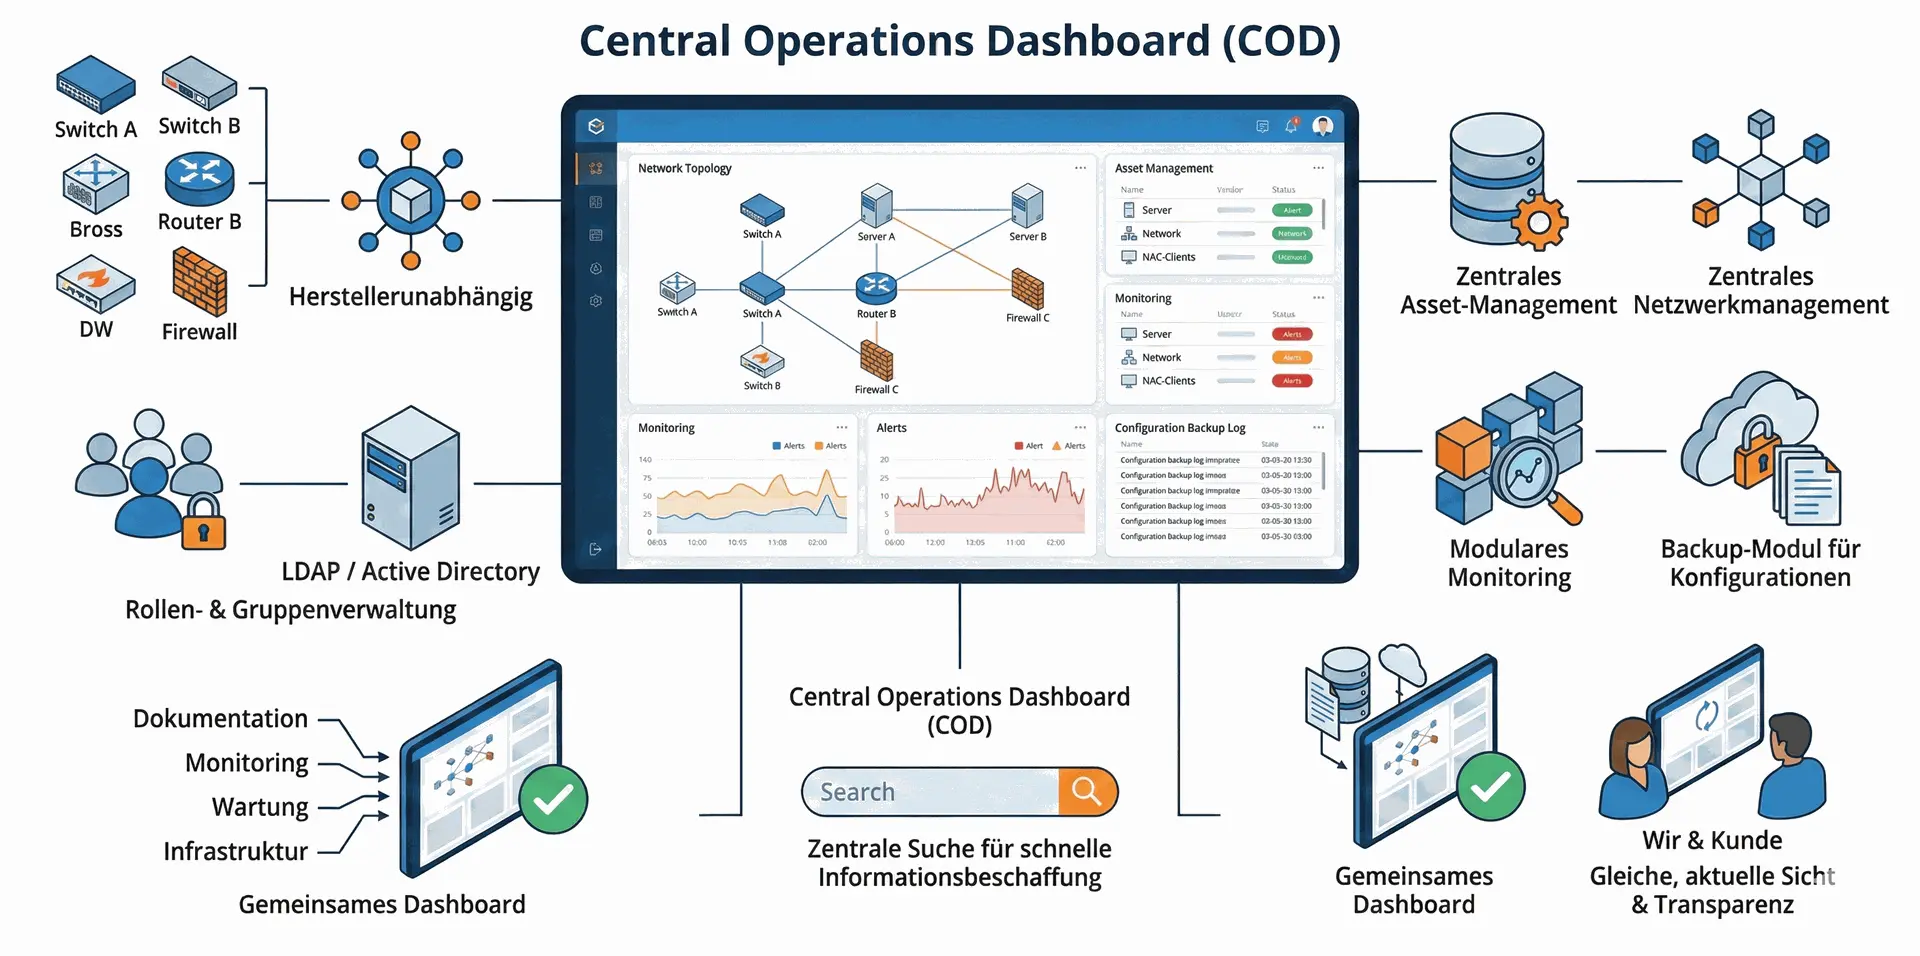
To manage the multitude of manufacturers (switches, routers, firewalls etc.) sensibly, we use the Central Operations Dashboard (COD).
👉 Central Operations Dashboard (COD) by extocode GmbH
Was macht COD aus?
- Central platform for a wide range of infrastructure systems from different manufacturers
- Vendor-independent – ideal for environments with many vendors
- Multi-Mandanten-fähig
- Rollen- & Gruppenverwaltung, inkl. Anbindung an externes LDAP / Active Directory
- Zentrales Asset-Management (Server, Netzwerk, NAC-Clients, etc.)
- Central network management with an overview of topology and details
- Modular monitoring – embedded into your existing monitoring
- Backup module for configurations (e.g. firewalls, switches, Linux/BSD systems)
- Central search for fast information retrieval, e.g. for 1st-level support
For our customers this means:
- Documentation systems, monitoring, maintenance calendar and infrastructure data come together in one shared dashboard.
- We and the customer see the same, current view of the infrastructure – ideal for transparency, operations, audits and collaboration.
Contact us today!
for your individual consultation!